WORK / 2026 / full-stack
inbo
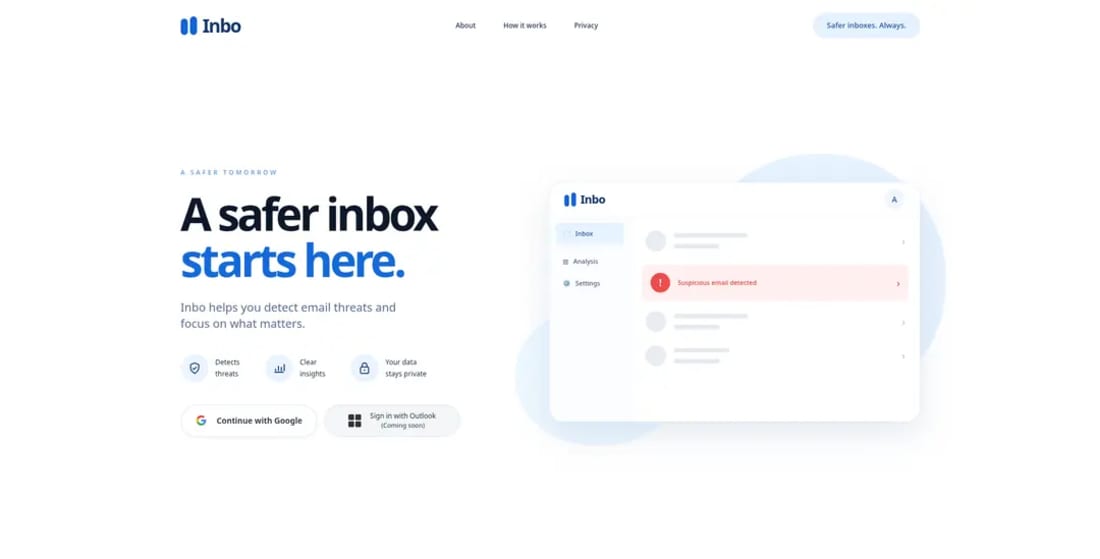
An email investigation workspace for spotting phishing, impersonation and suspicious sender infrastructure.
- ROLE
- Backend + integration + AI
- TIMELINE
- Hackathon MVP
- STACK
- Next.js · JavaScript · MongoDB · Gmail OAuth 2.0 · Groq
The problem
The problem
Phishing and business email compromise are difficult to investigate from a normal inbox because the useful clues are spread across headers, authentication results, URLs and sender infrastructure.
What I built
What I built
I built a Gmail OAuth based workflow that fetches messages directly, parses headers and URLs, exposes a message-level investigation view and uses an LLM for domain lookalike analysis.
How it works
How it works
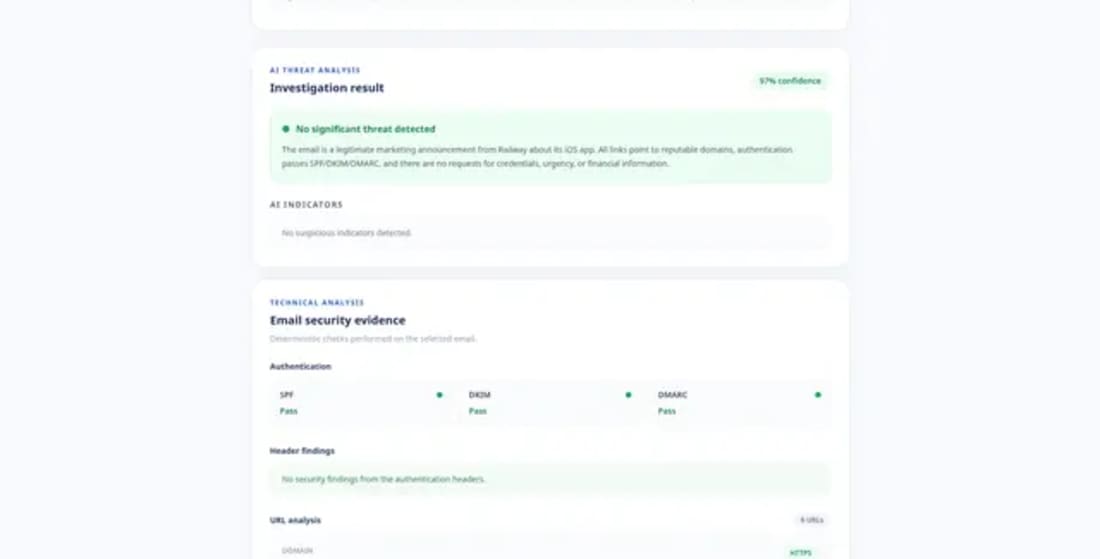
The Next.js app authenticates with Google, fetches readonly Gmail data, sends the message through parser and analyzer helpers, and presents security signals such as SPF, DKIM, DMARC and sender clues.
Challenges and what I'd change
Challenges and what I'd change
Traditional email security solutions can identify suspicious emails, but users often receive limited forensic context about why an email is suspicious, where it originated, what infrastructure was involved, or which domains and links should be investigated. Manually downloading .eml files and analyzing headers, authentication records, URLs, domains, and IP information is also difficult for non-specialist users. There was a need for a platform that could simplify this investigation process while providing deeper technical evidence instead of only a basic phishing/not-phishing classification.
Result
Result
PhishTrace provides an integrated email forensic investigation workflow. Users authenticate with Google OAuth 2.0 and access their emails directly through the Gmail API, eliminating the need to manually download and upload email files. When an email is selected, the platform extracts and analyzes headers, authentication information, URLs, domains, IP/relay data, and other indicators. AI-powered analysis is then used to correlate these signals and generate a structured investigation report with risk indicators and forensic insights. This combines automated email analysis, infrastructure intelligence, and AI-assisted investigation into a single workflow.
Visual notes
Screenshots